Welcome To The Hacker Club 4U

On This Blog Now You can get knowledge about how to to do hacking and also Know how to prevent from hacking and know many tips And tricks of computer and internet

Hacking

Click Here To Know Many Tricks and Tips Of HACKING facebook,twitter and other accounts and passwords

Hacking Safety And Security

Click Here to know how to protect your computer and inetrnet from hacking and know hacking safety and security tips and tricks

Facebook And Twitter

Click On Picture For TWITTER And Click On This Tittle For FACEBOOK .Hacking And Security Tips Of facebook and twitter.Know how to byepass facebook login and twitter login

Gmail And Yahoo

Click On Above Picture For GMAIL Hacking And Security Tips . And.Click On This Title For YAHOO Hacking and security tips


HOW TO: Add social networking buttons

This weeks blog how to is answering the following question that Shayna sent in: 


"I love how you have your facebook, twitter, email, and feeder buttons to follow you using pictures and it opens to the link, could you share how you accomplished that?"
 
Shayna also wanted to have them in a square, as I have done with the buttons on Someday Crafts, so I am going show you how to add the buttons linked to your social networking sites and then also how to arrange them into a square.
 
Here we go:
First off you will need to search for the icon that you need (easiest way is via Google Image Search), or you can right click the buttons below that you need and save them to your desktop, make sure to name them so you can recognize them (which is important later down the road, so for the ones below I have them named, FEED, FACEBOOK, TWITTER, MAIL_ICON).

These icons have been sized to 52 px x 52 px which is a good size for your sidebar, you can resize images in most photo editing software.

To add these to your sidebar:
First create a post as usual.  Click the Insert Image button.

In the pop-up window click Browse and locate the images on your desktop, click open and then insert them into your post.
Next you will want to right click on the Layout tab and click open in new tab (or new window if you have an older Internet Browser).
Go to that tab.  Click Add a Gadget in your sidebar.
In the pop-up window, select HTML/Javascript.

In the Configure HTML/JavaScript box, type in your Title (I used "I'm Social!") and then you will need to type this code for each image, so if you have four images, paste it four times and replace with your info:
Where do you get your Website URL?  Go to your Facebook page or other site (make sure you are logged out), select the address in the address bar and paste into the code.  If you are trying to find your Feedburner address, go to your account, you should be able to find it in there (it will start with: http://feeds.feedburner.com/ - mine is http://feeds.feedburner.com/733blog).

Where do you get your image URL? Go back to your other tab where we inserted the images.  Click on Edit HTML.
Don't get overwhelmed.  You will see a bunch of gobbly-gook.  You need to look for the image sources (if you have 4 images, there will be 4 image sources).

The easiest way to do this is to hit CTRL-F.  In the Find box type in src= and click next.  You want to select the info between the quotation marks after src=, now copy and paste it into the correct source spot in your Configure HTML/Layout Box.  If you have another image, click next on your Find box.  Continue doing this until you have all of your image URL's.  You can now close out your Post tab (don't hit Publish Post, just X out the tab - you don't even need to save the post if you are confident you did this right).

This is how it will look:
If you are OK with the images being in a row, you are done!

If you have 4 images and want them in a square shape as Shayna has requested, continue reading:
Open your html/javascript box.
Click on Rich Text.
It will look like this (I somehow managed to forget to put a space between the mail button and the feed button in this screenshot. If you want spaces between your icons, place your cursor between any two icons, click and hit the space bar).
Insert your cursor between the Facebook button and the Mail button and hit Enter.
Now it looks like this (notice the missing space between the mail and feed icon?):
Hit Save and you are done!
 Here is how it will look:
NOW YOU'RE DONE!

I hope this isn't too confusing.  Please feel free to ask questions.  OR, if you want me to do this for you, just send an email to 733blog (at) gmail.com.  For $15 I'll get it done!

I sent these directions to Shayna to give them a try and make sure they were clear and here was her response:

"I did it!!!!!!!!!!!!!!!!! OMG thank you so much, I'm still tweaking with the colors and pics I want to use but I have it done for now..."


HOW TO: Add sponsors buttons to your blog


I've had several people question how to add a sponsors button when the sponsor does not send html code, just the image.
 
Good news: it is super easy! {I always say that, don't I?  I can't help it! It's true.}
 
First, save the sponsors button to your computer desktop with an easily recognizable name - i.e. use the shop or blog name. 
 
Create a post as usual. Click the Insert Image button.


In the pop-up window, click Browse and locate the image on your desktop, click open and then insert it into your post.


Next you will want to right click on the Layout tab and click open in new tab (or new window if you have an older Internet Browser).
Go to that tab. Click Add a Gadget in your sidebar.
In the pop-up window, select HTML/Javascript.
In the Configure HTML/JavaScript box, type in your Title (something like "These Sponsors are Amazing") and then you will need to type this code for each image, so if you have four sponsor images, paste it four times and replace with your info:
Where do you get the Sponsor Website URL? Simply type in the address of the Etsy shop or blog that should open when the button is clicked.

Where do you get your image URL? Go back to your other tab where we inserted the images. Click on Edit HTML.
Don't get overwhelmed. You will see a bunch of gobbly-gook. You need to look for the image source(s) (if you have 2 images, there will be 2 image sources).
The easiest way to do this is to hit CTRL-F. In the Find box type in src= and click next. You want to select the info between the quotation marks after src=, now copy and paste it into the correct source spot in your Configure HTML/Layout Box. If you have another image, click next on your Find box.

You can now close out your Post tab (don't hit Publish Post, just X out the tab - you don't even need to save the post if you are confident you did this right).

Save your gadget and you are done.

What if you want to add another sponsor, but don't want a new gadget?  That is fine (and easier then having 20 sponsor gadgets!).  Just open up our sponsor gadget and paste in the html code with a space or break in between the first and second code. You can add as many buttons to the one gadget as you want!
If you have any questions, feel free to leave me a comment.

Facebook Password Hacker and Cracker

Facebook password Hacker


Facebook password Hacker,Facebook password Cracker or Facebook password extractor you might have heard these names.Yes these all are paid softwares which some website's claim that they will hack a Facebook password on typing the User ID.If you believe what they say then you are just wasting your time and money.These all softwares are fake Even I receive tons of daily emails asking for such email hacking software. So, I am writing this article to inform you reality of such email hacking software or can say password hacking software


Recently i came across a site which was claiming that With their free hacking tool you can obtain the password to nearly any profile on facebook.com,Is it possible?The answer is no.Guys, i want to tell you that there is no such Facebook hacking software. Totally depressed?? I am sorry to say, but this is true. There is no such email hacking software. So stop searching for such email hacking software. Stop fooling yourself. Just use your sense guys. If there exists such a software, will there be any security on web. And all expert engineers at Google, Yahoo and other services are not mad. They are all engaged in ensuring security of their customers ie email account owners. So, no such software exists.


What about Facebook password Hacking services?
Many sites on the internet claim to sell softwares/programs to hack email passwords. I know most of you are aware of this. These sites also boost that their software can hack email passwords with in minutes. Some sites also claim that they can hack any one’s password for money (say $100 or 200$). Never believe these sites. They are all scam,Most of Password Hacking services claim that they have a Password decryter or encrypter,They ask you to type an Id to Hack,they show you the hash form of the passwords and tell you to buy a software in order to reveal the password but when you make the payment the software dont work and you loose your money, I can dare challenge anyone who claims to hack an email, using a software program. In fact when I was a newbie in the field of Hacking, I have spent many sleepless nights in search of an Email hacking software. Finally I ended up only with frustration and nothing more than that. I don’t want my readers to commit the same mistake which I did. So, never believe those scam sites and empty your pockets by spending on useless softwares.

What are real ways of Facebook Hacking?
With my experience of almost 5 Years in this field of Hacking and Internet security i suggest you 4 real methods which can Hack a facebook password, I have posted these four of these methods in my post 4 ways on How to hack facebook password

How to Crack a Wi-Fi Network’s WEP Password with BackTrack

You already know that if you want to lock down your Wi-Fi network, you should opt for WPA encryption because WEP is easy to crack. But did you know how easy? Take a look.
Originally published last year, we wanted to revisit Gina's awesome guide to cracking Wi-Fi WEP passwords for Evil Week. Alternatively, if you're not in a reading mood, check out the video version.

Today we're going to run down, step-by-step, how to crack a Wi-Fi network with WEP security turned on. But first, a word: Knowledge is power, but power doesn't mean you should be a jerk, or do anything illegal. Knowing how to pick a lock doesn't make you a thief. Consider this post educational, or a proof-of-concept intellectual exercise.
Dozens of tutorials on how to crack WEP are already all over the internet using this method. Seriously—Google it. This ain't what you'd call "news." But what is surprising is that someone like me, with minimal networking experience, can get this done with free software and a cheap Wi-Fi adapter. Here's how it goes.

What You'll Need

How to Crack a Wi-Fi Network's WEP Password with BackTrackUnless you're a computer security and networking ninja, chances are you don't have all the tools on hand to get this job done. Here's what you'll need:
  • A compatible wireless adapter—This is the biggest requirement. You'll need a wireless adapter that's capable of packet injection, and chances are the one in your computer is not. After consulting with my friendly neighborhood security expert, I purchased an Alfa AWUS050NH USB adapter, pictured here, and it set me back about $50 on Amazon. Update: Don't do what I did. Get the Alfa AWUS036H, not the US050NH, instead. The guy in this video below is using a $12 model he bought on Ebay (and is even selling his router of choice). There are plenty of resources on getting aircrack-compatible adapters out there.
  • A BackTrack 3 Live CD. We already took you on a full screenshot tour of how to install and use BackTrack 3, the Linux Live CD that lets you do all sorts of security testing and tasks. Download yourself a copy of the CD and burn it, or load it up in VMware to get started. (I tried the BackTrack 4 pre-release, and it didn't work as well as BT3. Do yourself a favor and stick with BackTrack 3 for now.)
  • A nearby WEP-enabled Wi-Fi network. The signal should be strong and ideally people are using it, connecting and disconnecting their devices from it. The more use it gets while you collect the data you need to run your crack, the better your chances of success.
  • Patience with the command line. This is an ten-step process that requires typing in long, arcane commands and waiting around for your Wi-Fi card to collect data in order to crack the password. Like the doctor said to the short person, be a little patient.

Crack That WEP

To crack WEP, you'll need to launch Konsole, BackTrack's built-in command line. It's right there on the taskbar in the lower left corner, second button to the right. Now, the commands.
First run the following to get a list of your network interfaces:
airmon-ng
The only one I've got there is labeled ra0. Yours may be different; take note of the label and write it down. From here on in, substitute it in everywhere a command includes (interface).
Now, run the following four commands. See the output that I got for them in the screenshot below.

airmon-ng stop (interface)
ifconfig (interface) down
macchanger --mac 00:11:22:33:44:55 (interface)
airmon-ng start (interface)

How to Crack a Wi-Fi Network's WEP Password with BackTrack If you don't get the same results from these commands as pictured here, most likely your network adapter won't work with this particular crack. If you do, you've successfully "faked" a new MAC address on your network interface, 00:11:22:33:44:55.
Now it's time to pick your network. Run:
airodump-ng (interface)
To see a list of wireless networks around you. When you see the one you want, hit Ctrl+C to stop the list. Highlight the row pertaining to the network of interest, and take note of two things: its BSSID and its channel (in the column labeled CH), as pictured below. Obviously the network you want to crack should have WEP encryption (in the ENC) column, not WPA or anything else.
How to Crack a Wi-Fi Network's WEP Password with BackTrack Like I said, hit Ctrl+C to stop this listing. (I had to do this once or twice to find the network I was looking for.) Once you've got it, highlight the BSSID and copy it to your clipboard for reuse in the upcoming commands.
Now we're going to watch what's going on with that network you chose and capture that information to a file. Run:
airodump-ng -c (channel) -w (file name) --bssid (bssid) (interface)
Where (channel) is your network's channel, and (bssid) is the BSSID you just copied to clipboard. You can use the Shift+Insert key combination to paste it into the command. Enter anything descriptive for (file name). I chose "yoyo," which is the network's name I'm cracking.
How to Crack a Wi-Fi Network's WEP Password with BackTrack

You'll get output like what's in the window in the background pictured below. Leave that one be. Open a new Konsole window in the foreground, and enter this command:
aireplay-ng -1 0 -a (bssid) -h 00:11:22:33:44:55 -e (essid) (interface)
Here the ESSID is the access point's SSID name, which in my case is yoyo. What you want to get after this command is the reassuring "Association successful" message with that smiley face.
How to Crack a Wi-Fi Network's WEP Password with BackTrack
You're almost there. Now it's time for:
aireplay-ng -3 -b (bssid) -h 00:11:22:33:44:55 (interface)
Here we're creating router traffic to capture more throughput faster to speed up our crack. After a few minutes, that front window will start going crazy with read/write packets. (Also, I was unable to surf the web with the yoyo network on a separate computer while this was going on.) Here's the part where you might have to grab yourself a cup of coffee or take a walk. Basically you want to wait until enough data has been collected to run your crack. Watch the number in the "#Data" column—you want it to go above 10,000. (Pictured below it's only at 854.)
Depending on the power of your network (mine is inexplicably low at -32 in that screenshot, even though the yoyo AP was in the same room as my adapter), this process could take some time. Wait until that #Data goes over 10k, though—because the crack won't work if it doesn't. In fact, you may need more than 10k, though that seems to be a working threshold for many.
How to Crack a Wi-Fi Network's WEP Password with BackTrack

Once you've collected enough data, it's the moment of truth. Launch a third Konsole window and run the following to crack that data you've collected:
aircrack-ng -b (bssid) (file name-01.cap)
Here the filename should be whatever you entered above for (file name). You can browse to your Home directory to see it; it's the one with .cap as the extension.
If you didn't get enough data, aircrack will fail and tell you to try again with more. If it succeeds, it will look like this:
How to Crack a Wi-Fi Network's WEP Password with BackTrack The WEP key appears next to "KEY FOUND." Drop the colons and enter it to log onto the network.

Problems Along the Way

With this article I set out to prove that cracking WEP is a relatively "easy" process for someone determined and willing to get the hardware and software going. I still think that's true, but unlike the guy in the video below, I had several difficulties along the way. In fact, you'll notice that the last screenshot up there doesn't look like the others—it's because it's not mine. Even though the AP which I was cracking was my own and in the same room as my Alfa, the power reading on the signal was always around -30, and so the data collection was very slow, and BackTrack would consistently crash before it was complete. After about half a dozen attempts (and trying BackTrack on both my Mac and PC, as a live CD and a virtual machine), I still haven't captured enough data for aircrack to decrypt the key.
So while this process is easy in theory, your mileage may vary depending on your hardware, proximity to the AP point, and the way the planets are aligned. Oh yeah, and if you're on deadline—Murphy's Law almost guarantees it won't work if you're on deadline.

To see the video version of these exact instructions, check out this dude's YouTube video.
http://www.youtube.com/watch?feature=player_embedded&v=kDD9PjiQ2_U


How To Download Picasa Web Albums Without Installing Picasa

Note: this post initially linked to a Greasemonkey script that no longer works, but it now offers an easier solution suggested in the comments.

Unlike other photo sharing sites, Picasa Web Albums offers a way to download an entire album, but that requires Picasa 2.5 or later. If you don't want to install the application or you use Mac or Linux, there are other ways to download a photo album.

For Firefox, you can use DownThemAll, probably the best download manager add-on. After installing the extension and restarting the browser, go to the album you want to download, click on the "RSS" link from the sidebar and you'll get the album's feed. Right-click on the page, select DownThemAll/DownThemAll in the contextual menu, expand the Filters section and check "Images". Don't forget to enter the folder where you want to save the photos.

Update:  comments to find a lot of interesting ways to download albums from Picasa Web.

60% Of Vista Code Is Broken, While Office Is Delayed Too


Up to 60% of the code in the new consumer version of Microsoft Vista operating system is set to be rewritten, announces Smarthouse. In an effort to meet a dealine of the 2007 CES show in Las Vegas Microsoft has pulled programmers from the highly succesful Xbox team to help resolve many problems associated with entertainment and media centre functionality inside the OS.

On a related note, Microsoft confirmed that it is also pushing the mainstream launch of Office 2007 to next year. The reason is that Microsoft wants to launch Office and Vista in tandem.

So the word of the week for Microsoft was DELAY. But what if the problems are so difficult to solve that they need another year? They're working for Windows Longorn since 2003, that's 3 years ago, and 60% of the code they wrote needs to be rewritten. I think this needs almost 2 years, so the best thing to do is set a new deadline: December 2007.

How To Crack Your Windows Password


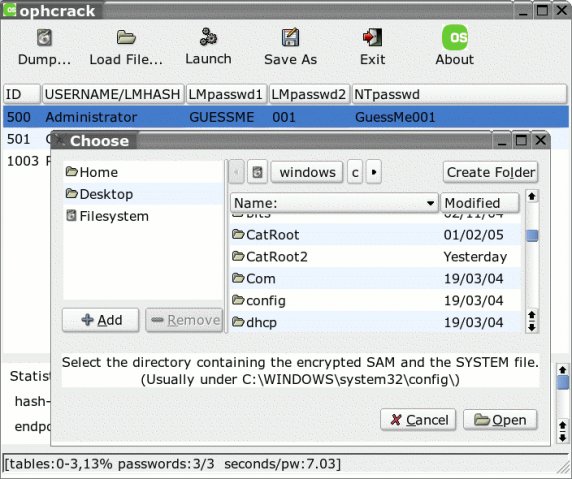
If you forgot your Windows password and you don't want to reset it, you have a new option: Ophcrack LiveCD, a Windows password cracker that claims to be able to crack 99.9% of alphanumeric passwords in seconds. Ophcrack is based on a time-memory trade-off using rainbow tables, some precalculated data stored in memory. A rainbow table is a lookup table that is constructed by placing a plaintext password entry in a chain of keys and ciphertexts, generated by a one-way hash (a function that is easy to calculate but hard to invert). The end result is a table that contains statistically high chance of revealing a password within a short period of time, generally less than a minute.

Minimum amount of RAM required: 256MB.
Recommended amount of RAM: 512MB.

Download Ophcrack Live CD

Recommend us on Google!

Share

Twitter Delicious Facebook Digg Stumbleupon Favorites More